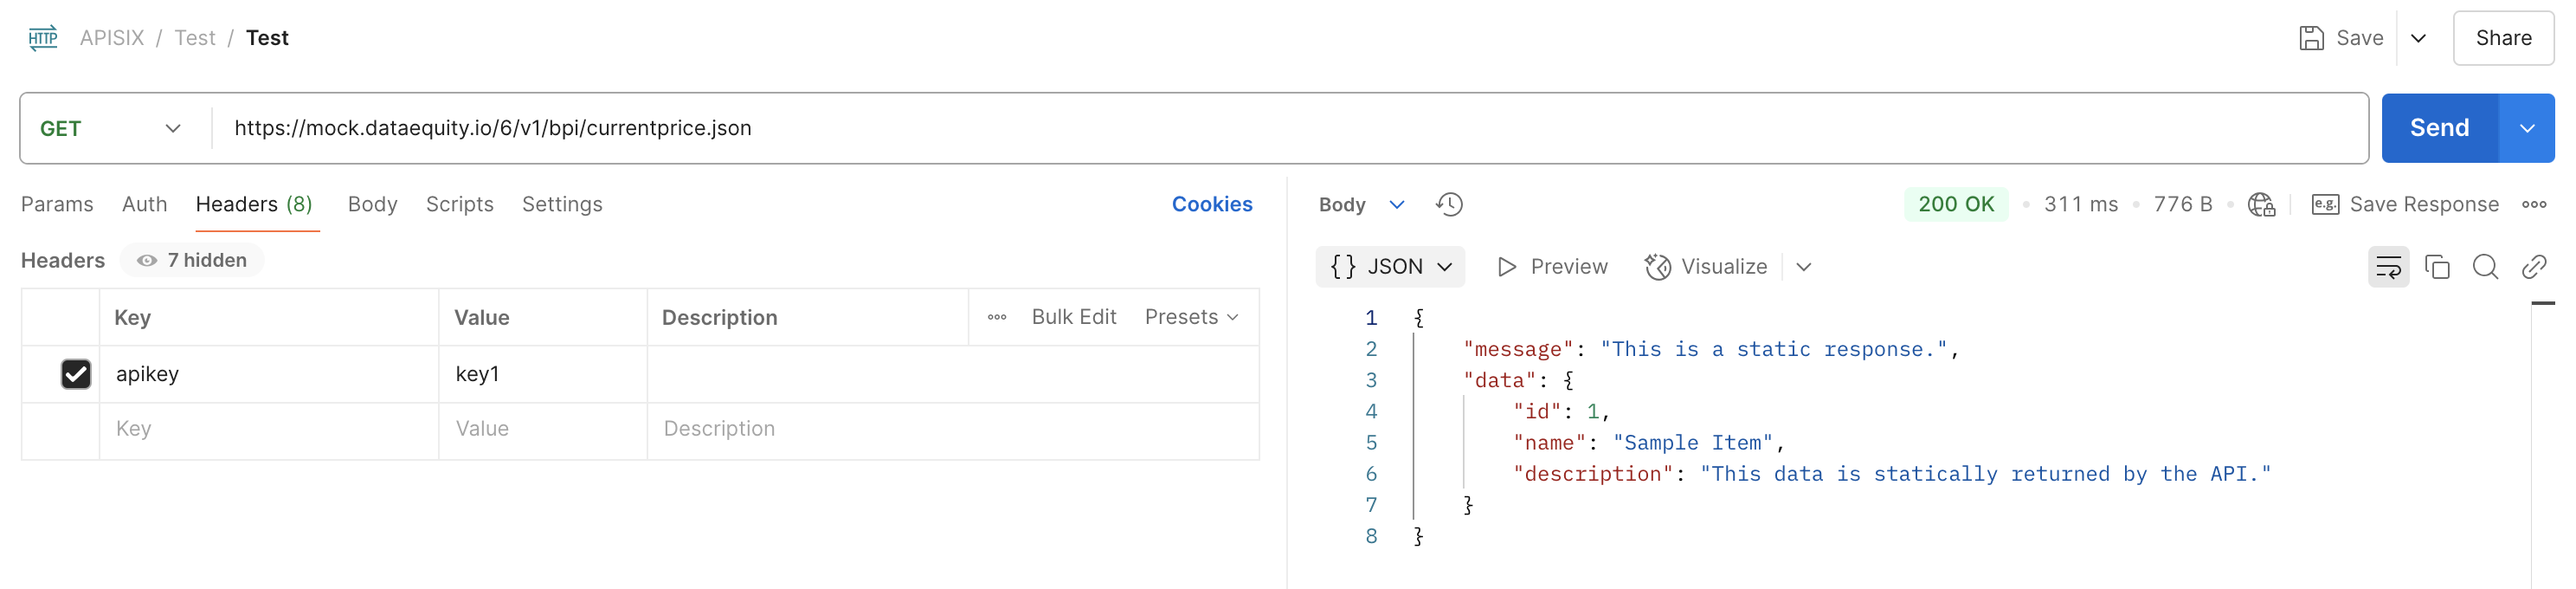
API Key Policy
The API Key Policy is designed to secure your API by requiring clients to present a valid API key with each request. This helps control access and ensures that only authorized users can interact with your API.
Key Features
- Access Control: Restrict API usage to clients who provide a valid API key.
- Security: Prevent unauthorized access by validating the API key against a configured list or service.
How It Works
- Client Request: When a client makes an API request, the request must include the
apikeyheader with a valid key. - Validation: The API policy intercepts the request and checks the provided API key.
- Access Decision:
- If the API key is valid, the request is forwarded to the backend or mock service.
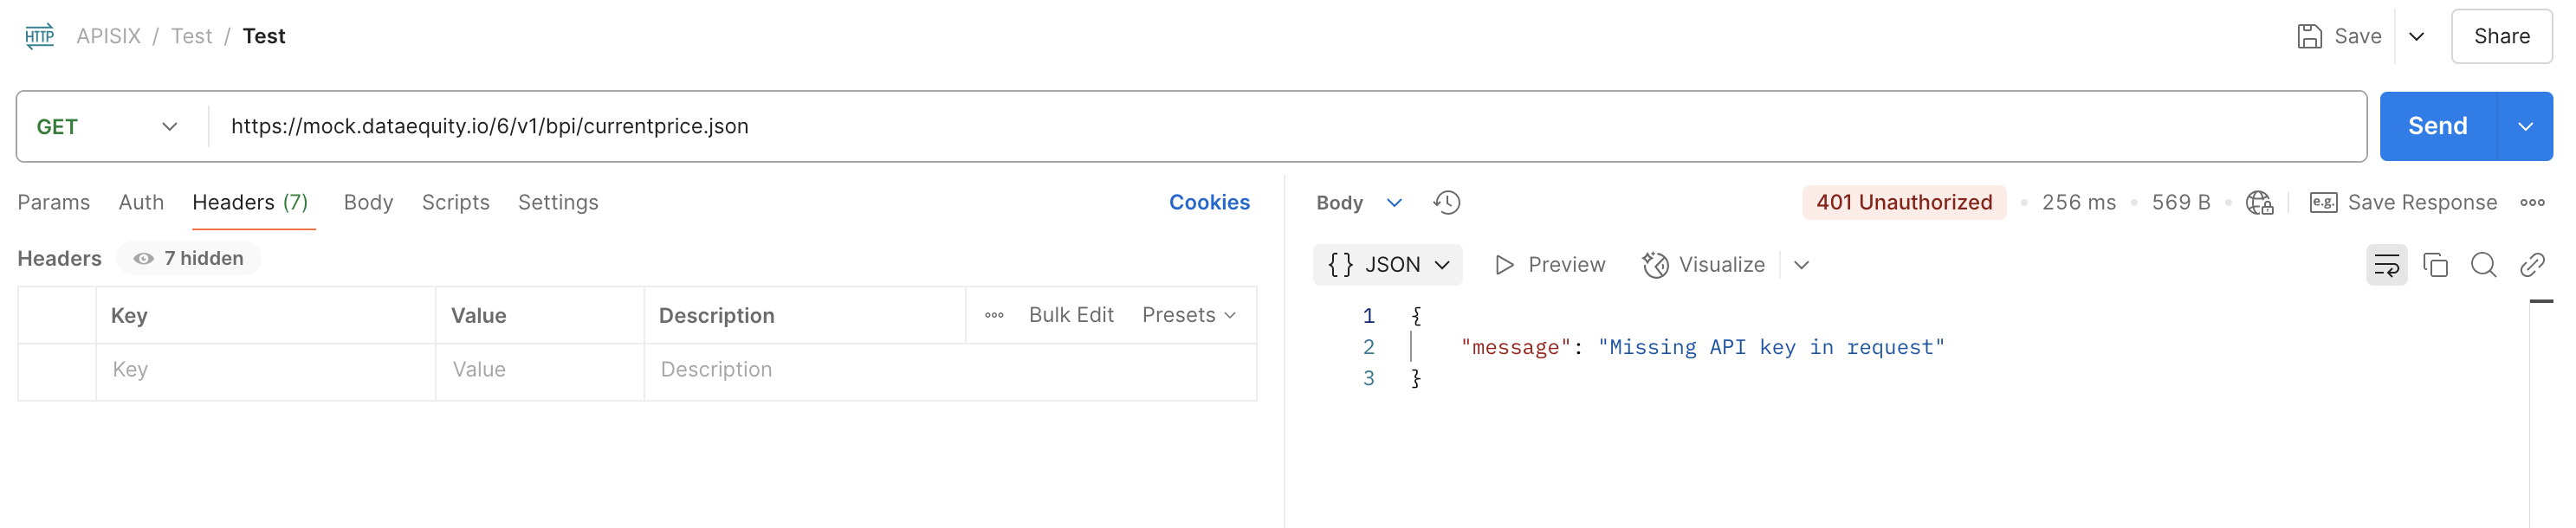
- If the API key is missing or invalid, the request is rejected, and an appropriate error response is returned.
Example Usage
When the API Key Policy is enabled, clients should include the header as shown below:
apikey: your-valid-api-key-here
Steps
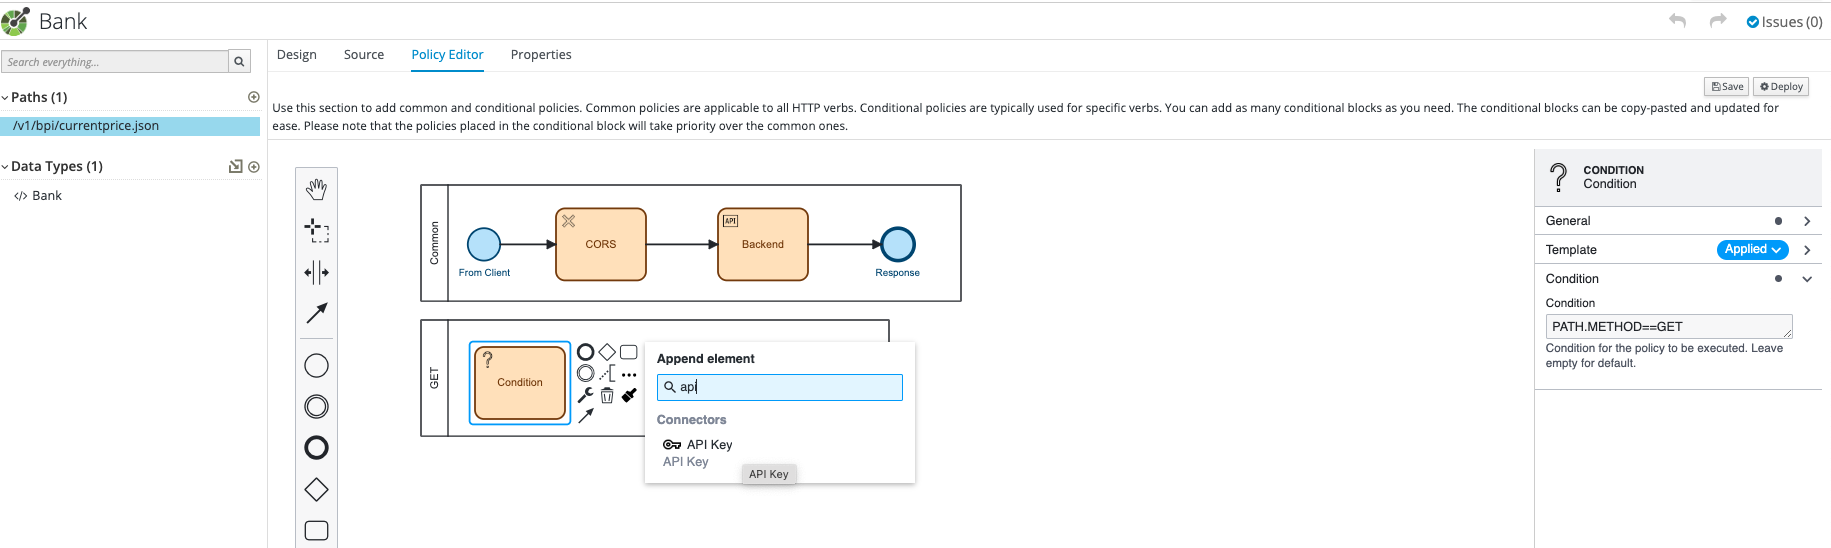
- Append the API Key policy
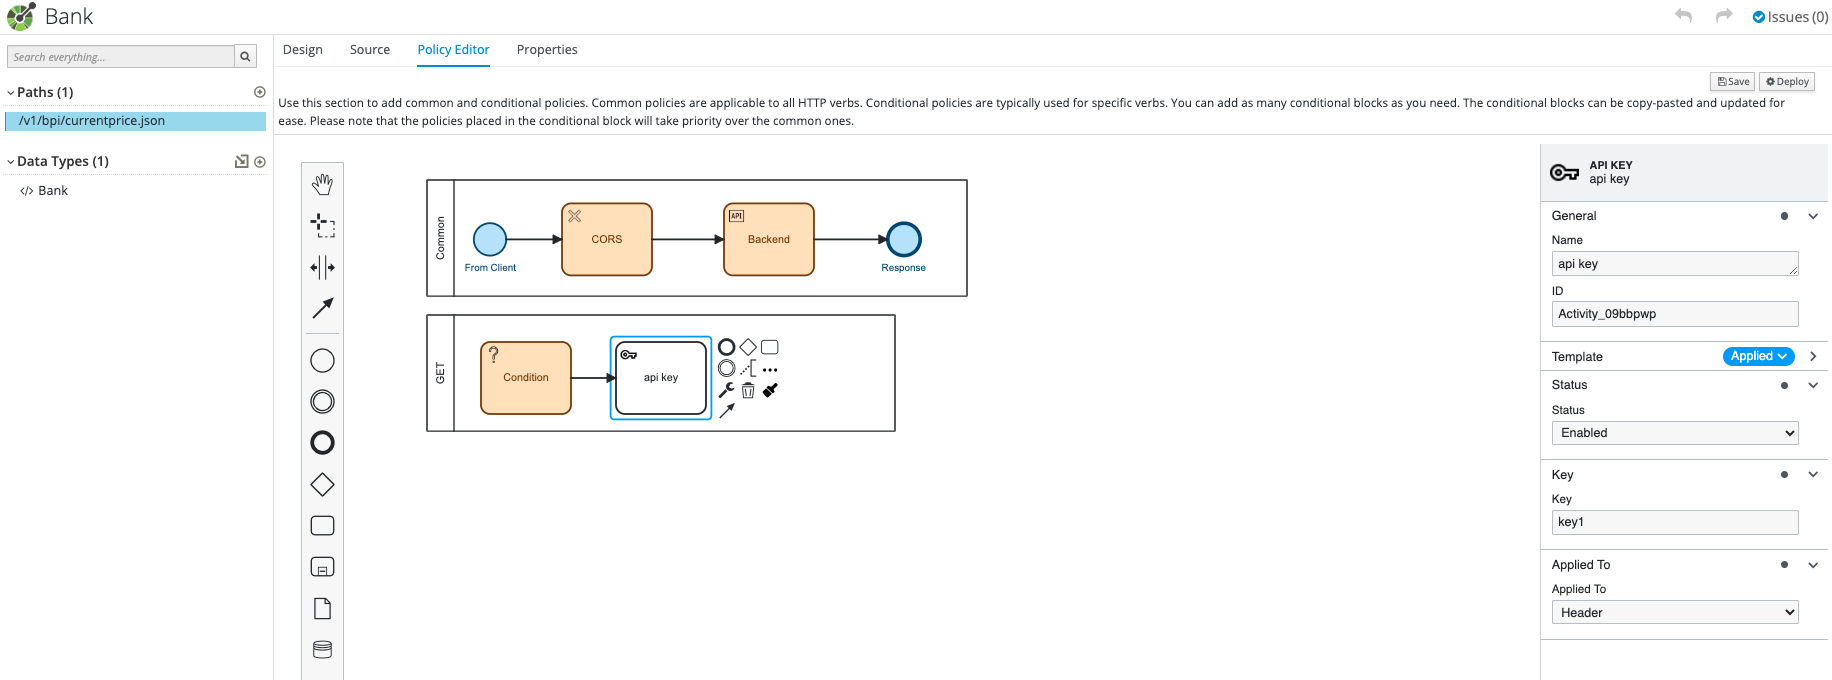
- Add a value for the property Key
- Test without key
- Test with key